



1. Observe
Collect the context around the asset.
Gather the signals around a case.
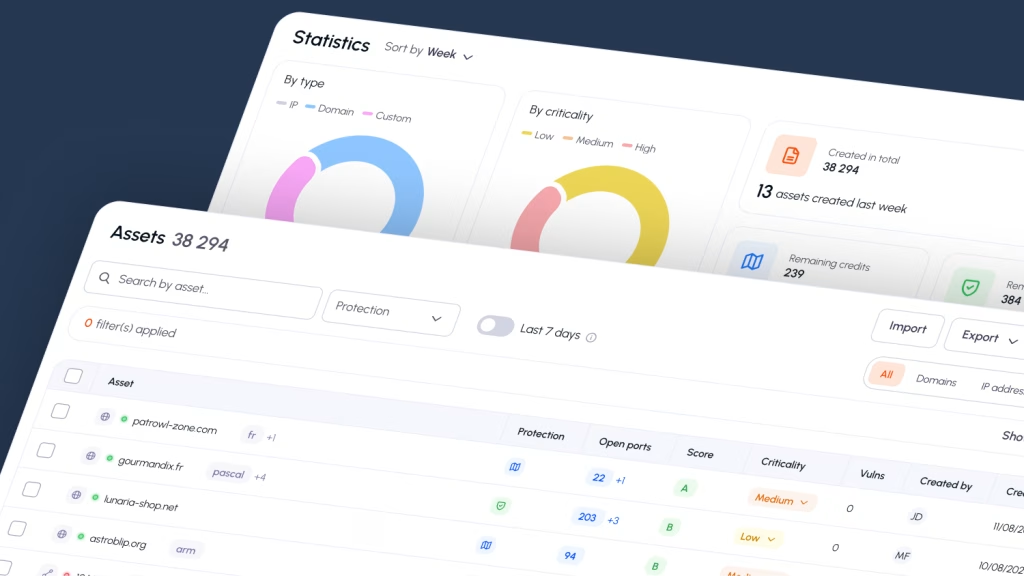
Patrowl starts from what is actually known about the asset and the threat.
collect asset data, technologies and exposure
pull in vulnerability, CVE and exploit intelligence
bring in test history and previously captured evidence
Result: every decision starts from real, current context, not assumptions.