Agentic AI Penetration Testing, validated by experts

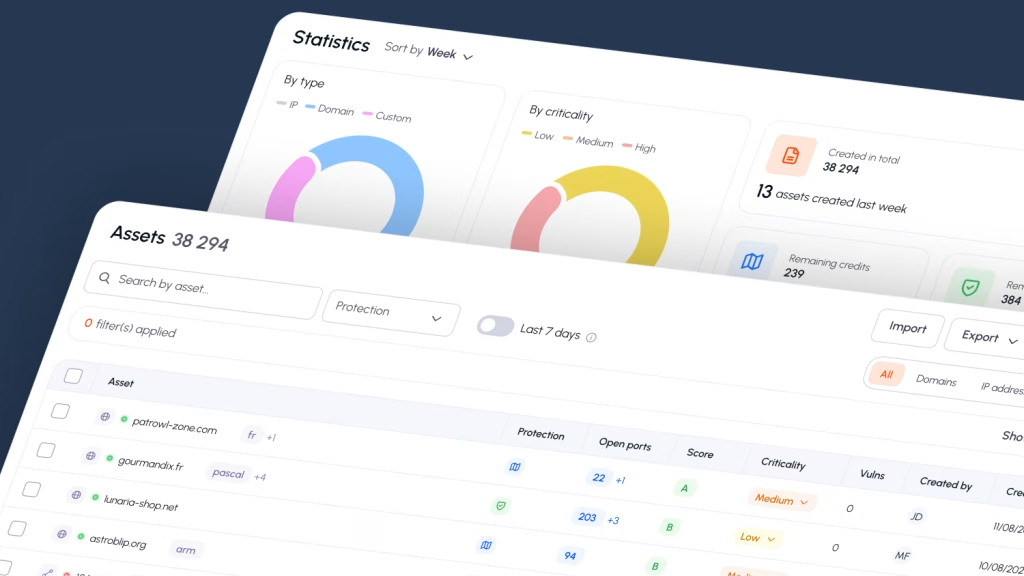
Patrowl's AI agents test your entire external attack surface every day, and a certified pentester validates every finding before it reaches you.

AI correlates

Our AI agents link assets, technologies, threats and past tests, and choose the next step.

Automation executes

Our engine runs every repeatable test on every asset, every day.

Experts validate

Certified pentesters prove and validate each finding before it reaches you.

Trusted by

CAC 40 companies, public institutions and scale-ups

A solution built by pentesters and cybersecurity auditors.

  • Construction & infrastructure10,000+ employees Colas
  • Mutual health insurance10,000+ employees MGEN
  • EU public finance1,000–5,000 employees European Investment Bank
  • Audit & advisory10,000+ employees Forvis Mazars
  • Ride-hailing50–200 employees Heetch
  • Local government1,000–5,000 employees Brest Métropole
  • SaaS & payments1,000–5,000 employees Xplor
  • Digital archiving10–50 employees Arkhineo
  • Public hospital1,000–5,000 employees CH Avignon
  • Beauty booking SaaS200–500 employees Planity
  • Industrial e-commerce10–50 employees 123 Roulement
  • +120clients

From millions of assets to the findings that matter

Our agents sort through the volume, so your teams only receive findings a pentester has checked and signed.

  1. 3M+Exposed assets analyzedAcross the Patrowl platform
  2. 100%Findings validated by pentestersExpert-reviewed and signed
  3. 24–48hTo your first validated findingsWith actionable remediation guidance
  4. 3×Faster vulnerability remediationCompared with the measured baseline

Platform figures, 2026.

Patrowl — Trio (scoped embed)

← scroll →

Automation · continuous pentest Agentic AI · correlate, triage, exploit Human validation · complex & critical

How Agentic AI Penetration Testing works

  • 1. Observe

    Collect the context around the asset.


    Gather the signals around a case.

    Patrowl starts from what is actually known about the asset and the threat.

    • collect asset data, technologies and exposure

    • pull in vulnerability, CVE and exploit intelligence

    • bring in test history and previously captured evidence

    Result: every decision starts from real, current context, not assumptions.

  • 2. Correlate

    Connect signals that belong together.


    Connect signals that belong together.

    The agent looks for relationships between exposure, vulnerabilities and previous evidence.

    • link a CVE to the technology in use

    • connect several findings to the same asset

    • reuse earlier test evidence when it changes the scenario

    Result: related signals become one security question.

  • 3. Decide

    Choose the next useful action.


    Choose the next useful action.

    The agent uses the available evidence to guide what should happen next.

    • request more context when evidence is incomplete

    • route a known scenario to automated testing

    • flag a complex case for expert review

    Result: the next step follows the evidence instead of a fixed sequence.

  • 4. Execute or Escalate

    Send the action to the right execution path.


    Send the action to the right execution path.

    Patrowl separates analysis from offensive execution.

    • run repeatable controls through the testing engine

    • keep sensitive actions under human decision

    • move business logic or complex attack paths to a pentester

    Result: automation handles repeatable work while experts keep control of high-judgment cases.

What context does Agentic AI use?

Four context layers that change the next decision.

Asset context Domains IPs Web apps APIs Exposed services Tech Vulnerability context New CVEs Public exploits CWEs Known weaknesses Threat intelligence Testing history Previous tests Validated evidence Retest status Earlier findings Investigation context Auth issues Privilege escalation Attack paths Sensitive data AGENTIC AI reasons on context NEXT DECISION Chase a sensitive-data exposure shaped by investigation context

The agent uses these layers to guide the next action. It does not replace the testing engine, your security tool stack or human expertise.

Vladimir Kolla - Patrowl Co-fondeur

Agentic AI vs rules-based penetration testing automation

When fixed automation is not enough

Criterion
Rules-based automation
On-demand AI pentest
Patrowl continuous agentic pentest
Coverage
All assets, standard checks
The targets you order
Every asset, every day
Depth of testing
Known checks
Deep on the chosen target
Deep where it changes, continuous everywhere
Rhythm
On a schedule
Each time you order a test
Every day, plus every release and new threat
Consistency over time
Repeatable results
A fresh run for each test
Kept until fixed and retested
Expert validation
Alerts for your team to triage
Depends on the provider
Every finding signed by a pentester
Time to first results
After setup
After each order
24 to 48 hours, then every day

RESEARCH

Our agents also discover new vulnerabilities

Our research agents study the open-source code your sites rely on. Each discovery is confirmed by a pentester, shared with the maintainer and fixed before publication. Recent CVEs credited to Patrowl:

  • CVE-2026-6453

    SQL injection
    CubeWP Framework (WordPress)

  • CVE-2026-10039

    SQL injection
    Frontend Admin (WordPress)

  • CVE-2026-6225

    Time-based blind SQL injection
    Taskbuilder (WordPress)

  • CVE-2026-3523

    SQL injection
    Apocalypse Meow (WordPress)

  • CVE-2026-6455

    CSRF leading to file deletion
    WP Contact Form 7 DB Handler

  • CVE-2026-6203

    Open redirect
    User Registration & Membership (WordPress)

EXAMPLE OF A ZERO-DAY FOUND BY AI PENETRATION TESTING OPEN SOURCE Public plugin code A WordPress component your assets depend on SQLi SQL Injection CVE-2026-6453 Medium · CVSS 6.5 · CWE-89 Authenticated (Subscriber+) CubeWP Framework ≤ 1.1.30 WHAT PATROWL USES Asset context Vulnerability context Severity Exploitability Remediation history Previous tests AGENTIC AI Context + decision What should happen next? automate · gather context · escalate REPEATABLE CASE AUTO Automated retest Replay relevant control Confirm exploitability SENSITIVE CASE EXP Pentester review Complex exploitation Manual validation Remediation Reported to the maintainer Fixed upstream · users update Reported & fixed — credited to Patrowl Validated by a pentester before disclosure WHAT THE SECURITY TEAM GETS Risk · SQL injection Priority · Medium Evidence ready Fix guidance Retest · Confirmed fixed

EXAMPLE OF A ZERO-DAY FOUND BY AI PENETRATION TESTING

OPEN SOURCE · PUBLIC CODE

Public plugin code

Patrowl’s agents hunt unknown flaws in the CubeWP Framework, a WordPress component your assets depend on.

FINDING

SQL Injection — CVE-2026-6453

Medium · CVSS 6.5 · CWE-89 · authenticated (Subscriber+). Affects CubeWP Framework ≤ 1.1.30.

AGENTIC AI · CONTEXT + DECISION

What should happen next?

The AI brings together asset context, vulnerability intelligence, severity, exploitability, remediation history and previous tests, then decides: automate, gather more context, or escalate.

Asset contextVulnerability contextSeverity ExploitabilityRemediation historyPrevious tests
REPEATABLE CASE

Automated retest

Replay the relevant control and confirm exploitability.

SENSITIVE CASE

Pentester review

Complex exploitation and manual validation by an expert.

REMEDIATION

Reported, fixed and credited to Patrowl

Reported to the maintainer and fixed upstream. The finding was validated by a pentester before disclosure.

WHAT THE SECURITY TEAM GETS
Risk · SQL injection Priority · Medium Evidence ready Fix guidance Retest · Confirmed fixed

Fewer findings, more fixes

"The race for vulnerability counts is a poor metric: It rewards whoever shows the most, not whoever reduces the risk. The conversation needs to come back to remediation, and that is also the best way to show what triage actually delivers."

Florent Montel – Chief Hacking Officer & Patrowl Co-foundeur

CUSTOMER STORIES

Security teams that test every day with Patrowl

  • “We now receive high-quality, verified vulnerability results continuously, allowing our engineers to act immediately. Patrowl has made our security efforts more efficient, collaborative, and impactful.””

    Xplor
  • “With Patrowl, one click is enough to place an asset under surveillance. We can manage critical vulnerabilities while providing solid proof of compliance — all with a small team”

    Brest Métrople
  • “Continuous pentesting is an innovative approach that enables us to continuously assess our exposure and keep pace with the fast-changing nature of today’s enterprise IT environments.”

    Arkhineo
  • “Continuous pentesting is […] an innovative solution, perfectly aligned with the fast-paced evolution of today's enterprise IT.”

    MGEN
  • “It took just two days to deploy Patrowl across all public-facing assets of the Heetch group, following a successful proof of concept.”

    Heetch

TRUST & CONTROL

Built to attack. Controlled to protect.

Patrowl combines agentic AI, controlled offensive execution and certified human expertise to keep every test scoped, traceable and safe for production.

  • Safe testing
    AI can recommend the next action, but offensive execution remains bounded by Patrowl’s controlled capabilities, testing rules and production safeguards.

  • Human oversight
    Certified pentesters handle sensitive decisions, complex attack paths and validate the evidence behind each finding(OSCP, OSWE, OSWP, OSCC, PNPT, CREST CRT and ISO 27001 Lead Auditor)

  • Security & traceability
    Context, decisions, findings and retests remain connected, while sensitive data is protected through French hosting, encryption and enterprise access controls.

  • Recognition & standards
    Patrowl’s testing approach builds on recognized frameworks such as PTES, OWASP, NIST and ANSSI guidance, alongside external industry recognition.

Certified expertise

Every vulnerability is validated by a certified pentester

Our offensive team holds the certifications security teams trust, from web exploitation to audit.

  • OffSec Certified ProfessionalOffSec OSCP
  • OffSec Web ExpertOffSec OSWE
  • CREST Registered Penetration TesterCREST CRT
  • Practical Network Penetration TesterTCM Security PNPT
  • OffSec Wireless ProfessionalOffSec OSWP
  • OffSec CyberCore CertifiedOffSec OSCC
  • ISO/IEC 27001 Lead AuditorISMS audit ISO 27001
  • Testing frameworksApplied to every engagement Methodologies

OUR OFFERS

Two offers to cover your external exposure

EASM

External attack surface management

Map and monitor your external attack surface continuously, including assets your inventory has yet to list.

  • Continuous discoveryDomains, :subdomains, IPs, applications and exposed services.

  • Shadow IT:Assets linked to your organisation, beyond your current inventory.

  • Configuration and exposure checks: Services and settings that widen your exposure, flagged as they appear.

  • Emerging threats:The assets concerned by each new vulnerability, identified within hours.

Book a demo

Offensive security testing

Continuous automated penetration testing

Automation, agentic AI and certified pentesters test your exposed assets continuously and qualify what can truly be exploited.

  • Continuous offensive testing: Black-box and grey-box testing of your exposed assets.

  • Qualification: The real exploitability of each finding, confirmed and signed by a pentester.

  • Prioritisation: Your teams focus on the risks that matter most.

  • Remediation and retest:Fix guidance for every finding, and a one-click retest to confirm it.

Request a quote

Who is Agentic AI Penetration Testing for?

CISO / Head of Security

I need to…

  • reduce noise and false positive signals between alerts and action

  • understand why the next test matters

  • keep AI-assisted decisions traceable

What Patrowl brings: context, evidence and controlled escalation that improve the security posture of security teams.

SOC / VOC / CERT

I need to…

  • connect threat intelligence with exposed technologies

  • understand which signal deserves action

  • keep investigation context when a case escalates

What Patrowl brings: one path from threat signal to validation or expert review.

Vulnerability Management

I need to…

  • prioritize with more than a severity score

  • connect asset context with exploit data

  • route the right issue to remediation

What Patrowl brings: context-aware analysis before the next security action.

Offensive Security / Pentesters

I need to…

  • spend less time on repetitive correlation

  • receive better context before manual investigation

  • keep control of sensitive exploitation

What Patrowl brings: AI-assisted preparation without removing human judgment.

DevSecOps / Application Security

I need to…

  • understand how a change affects an exposed app

  • send known checks to automation or CI CD pipelines

  • keep complex application behavior under expert review

What Patrowl brings: adaptive routing between analysis, automation and experts.

Compliance / GRC

I need to…

  • keep a trace of how findings were analyzed

  • connect evidence to remediation and retesting

  • support audit reviews with documented decisions

What Patrowl brings: traceable context and technical evidence throughout the workflow.

Start Agentic AI Penetration Testing with Patrowl

Use AI for context, automation for repeatable execution and experts for deeper investigation.

FAQ — Agentic AI Penetration Testing

What problem does Agentic AI solve in penetration testing?

It helps when the next action depends on context. The agent connects asset data, vulnerability information and previous evidence before guiding the next step.

Is Agentic AI the same as fully autonomous pentesting?

No. Patrowl separates AI guidance from offensive execution. Unlike fully autonomous penetration testing, repeatable tests run through controlled engines, while complex or sensitive actions can move to human experts.

When is Agentic AI more useful than standard automation?

Standard automation works best when the test is already known. AI pentesting adds value when several signals or attack vectors must be connected, or when one result changes what should happen next.

Does Agentic AI replace penetration testers?

No. Human testers remain important for business logic, complex attack paths, exploit adaptation and sensitive scenarios.

Does AI Penetration Testing replace traditional pentesting?

No. Traditional pentesting remains useful for deep human investigation. Agentic AI helps with context, routing and repeatable analysis around that work.

Can Agentic AI test prompt injections?

Where an AI-enabled web app exposes relevant attack surfaces, prompt injections can become part of a scoped security assessment. Complex cases should still stay under expert control.

How can I trust an AI-assisted finding?

Patrowl keeps the analysis connected to the affected asset, technical evidence, previous test results and the final validation path. The process validates findings before they become actions and keeps validated exploitation separate from AI-only analysis.

Can Agentic AI work with my existing security process?

Yes. It can add context before automation, expert review, remediation or retesting without replacing the wider security workflow.